
A supplier passes its annual risk review in March. By September, a subcontractor change, a credit downgrade, and a missed audit have quietly moved that supplier into a different risk category, and nobody finds out until the next scheduled review, or until something breaks. This is the structural weakness in most supplier lifecycle management programs today: risk is treated as something you check periodically, not something you watch continuously.
Supplier risk management is the structured process of identifying, assessing, mitigating and monitoring the financial, operational, compliance, cybersecurity and geopolitical risks associated with supplier relationships. That definition has not changed. What is changing is how enterprises manage that process: periodic assessments increasingly need to be complemented by ongoing monitoring between formal reviews. This article explains the difference between assessment and monitoring, what continuous supplier intelligence actually tracks, how to build a workable risk scoring approach, and what enterprises should do differently starting now.
Key Takeaways
What Is Supplier Risk Management?
Supplier risk management is the systematic process of identifying, assessing, mitigating, and monitoring the risks that arise from an organization’s supplier relationships, anything that could prevent a supplier from meeting its contractual obligations or performance expectations. It typically follows a repeatable cycle: identify the risks a supplier relationship could introduce, assess each one by likelihood and potential business impact, decide how to mitigate or accept it, and monitor the relationship on an ongoing basis so new risks are caught as they emerge.
That last stage, monitoring, is where most programs are weakest. Many organizations run the identify-assess-mitigate steps well during onboarding and periodic review, then let the relationship run largely unwatched until the next scheduled check.
Supplier Risk Assessment vs Supplier Risk Monitoring
These two terms get used interchangeably, but they describe different activities with different purposes.
| Dimension | Supplier Risk Assessment | Supplier Risk Monitoring |
|---|---|---|
| What it is | A periodic, in-depth evaluation producing a risk score | Ongoing tracking of signals between assessments |
| Frequency | Scheduled: annual, semi-annual, or at onboarding | Continuous or near-real-time |
| Depth | Deep: questionnaires, document review, audits | Shallower but constant: alerts, signal changes |
| What it catches | The supplier’s risk profile as of the review date | Changes that occur after that date |
| Typical output | A risk score, tier, or approval decision | An alert, a flag, or a trigger for re-assessment |
Why Periodic Supplier Risk Assessments Create Blind Spots
A periodic review is a snapshot: accurate on the day it is taken, and gradually less accurate with every week that passes afterward. Supplier risk rarely stays still for a full year, or even a full quarter, between formal reviews. A financially stable supplier can face a liquidity event next quarter. A compliant supplier can quietly outsource part of its operations to a subcontractor nobody has assessed. A stable region can become volatile with little warning. None of that shows up until the next scheduled assessment, by which point the best response options are often already gone.
The gap between ambition and readiness here is wide. Deloitte’s 2024/5 Global Third-Party Risk Management Survey, covering 338 respondents surveyed between December 2024 and February 2025, found that 93% of responding leaders report low maturity in AI-enabled third-party risk management, even as most organizations are actively trying to adopt it. The same survey found that 42% of respondents believe AI-enabled automation could reduce their financial exposure following a third-party disruption by at least 20%, and close to half believe potential damages from a major third-party incident could exceed US$50 million.
The lag is rarely dramatic on any single day, which is part of why it goes unnoticed. A supplier’s on-time delivery rate might slip from 96% to 91% over two quarters, still within an informal comfort range, until it crosses a threshold nobody was watching. A certificate expires and the renewal paperwork sits in someone’s inbox for six weeks because no system flagged it. A supplier may begin requesting shorter payment cycles or advance-payment terms, which can warrant closer financial review when considered alongside other risk signals. Individually, none of these look urgent. Tracked as a trend rather than a point-in-time answer, they are exactly the kind of signal continuous monitoring is built to catch.
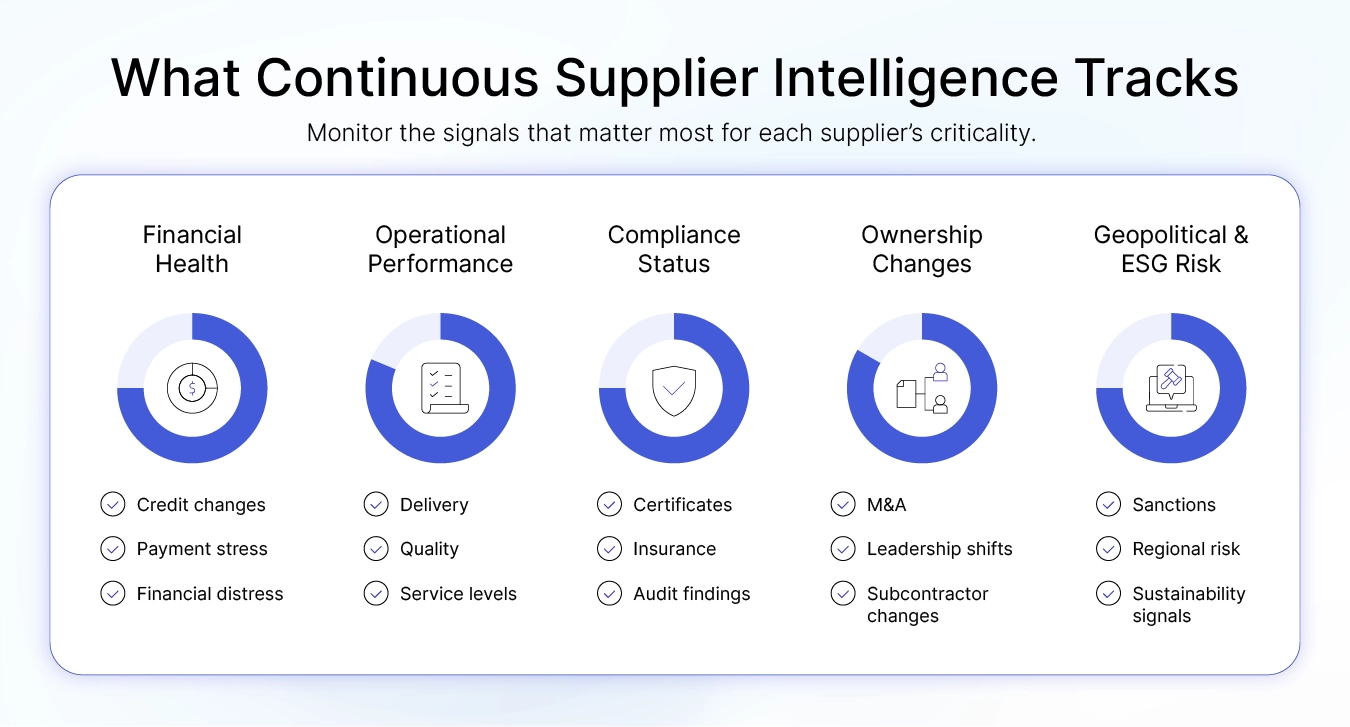
What Does Continuous Supplier Risk Monitoring Track?
Continuous supplier risk monitoring is the ongoing tracking of relevant supplier signals between formal assessments so material changes can be identified and reviewed earlier. Together, those signals create a more current layer of supplier intelligence.
How Should Enterprises Build a Supplier Risk Scoring Model?
A workable risk scoring approach does not need to be complex to be useful. A few design choices determine whether it actually gets used.
- Tier suppliers by criticality first. Not every supplier needs the same level of scrutiny. A single-source supplier for a critical component warrants closer, more frequent monitoring than a low-value, easily replaced vendor.
- Weight signals by relevance, not uniformly. Financial signals may matter more for a strategic supplier; compliance signals may matter more in a regulated category. A single generic score across all suppliers hides more than it reveals.
- Set clear trigger thresholds. A credit rating downgrade, a failed audit, adverse media coverage, or a significant delivery performance drop should each have a defined threshold that triggers a review, not a judgment call made after the fact.
- Route triggers to a named owner. An alert nobody is responsible for acting on is not risk management, it is a dashboard. Every trigger needs an accountable reviewer and a defined response window.
- Let monitoring escalate to assessment, not replace it. A material signal change should prompt a full reassessment, not just a noted flag. The two activities work together, not as substitutes for each other.
What Should Happen When a Supplier Risk Signal Is Triggered?
A scoring model only creates value if there is a defined process behind every trigger. Without one, alerts accumulate in a dashboard nobody checks, and the program quietly reverts to periodic review in practice even if it is called continuous monitoring on paper.
- Acknowledge and classify. The first step is confirming the signal is real and sorting it by severity, a minor documentation lapse is not the same response path as a credit downgrade on a single-source supplier.
- Assign a response window. Higher-severity triggers need a defined turnaround, days for a critical supplier, weeks for a lower-tier one, so a flagged risk does not sit unreviewed until the next status meeting.
- Decide the next action. Depending on severity, that might mean requesting updated documentation, opening a corrective action plan with the supplier, pausing new purchase orders, or triggering a full requalification.
- Close the loop back into the supplier record. The outcome, not just the alert, should update the supplier’s profile, so the next person reviewing that supplier sees the resolution, not just the original flag.
This is also where continuous monitoring earns trust internally. A program that generates alerts nobody acts on quickly gets treated as noise. A program where every trigger visibly leads to a decision, even a decision to accept the risk and move on, is the one procurement and risk teams actually rely on.
Supplier Due Diligence Still Matters
None of this reduces the importance of thorough supplier onboarding and due diligence at the start of a relationship. Continuous monitoring assumes a reliable baseline to monitor against, verified financial standing, confirmed certifications, a documented risk profile, established at onboarding. Without that initial due diligence, ongoing signals have nothing accurate to compare against. The sequence matters: rigorous due diligence establishes the baseline, and continuous monitoring tracks whether that baseline still holds as the relationship continues.
How to Move from Periodic Supplier Reviews to Continuous Monitoring
Moving from periodic to continuous does not require replacing an existing risk program. It requires layering monitoring on top of what already exists.
- Start with the highest-criticality suppliers rather than attempting full coverage on day one; the return on continuous monitoring is highest where a disruption would hurt most.
- Connect monitoring data back to sourcing and contract decisions, not just a standalone risk dashboard, so a rising risk signal can actually influence the next award or renewal.
- Keep periodic deep assessments on the calendar. Continuous monitoring catches change; it does not replace the depth of a full review.
- Assign monitoring ownership explicitly, by category or supplier tier, so a triggered alert has a clear person accountable for the next step.
Industry Considerations
The right monitoring intensity varies by sector. In oil and gas and chemicals, supplier qualification and HSE compliance documentation carry regulatory weight, so compliance and certification signals deserve continuous tracking, not just annual review. In pharmaceuticals, supplier qualification status and audit findings connect directly to inspection readiness, making documentation currency a continuous rather than periodic concern. In EPC and infrastructure, subcontractor and ownership changes matter most, since project delivery often depends on a chain of suppliers whose structure can shift mid-project without formal notice. In manufacturing, operational signals carry the most weight: a single-source supplier for a critical component can go from stable to constrained with little advance warning, and delivery and quality trends across multi-plant operations are often the earliest indicator that a supplier relationship is under strain.
SAFAL Insight
Most supplier risk conversations still center on the assessment: the questionnaire, the score, the approval decision. That is necessary, but it answers a narrower question than the one enterprises actually need answered, which is not "was this supplier low risk when we checked," but "is this supplier still low risk today."
The two questions sound similar and are not. Answering the second one works best when risk signals are connected to the supplier record and the sourcing, onboarding, performance and purchasing decisions they may affect.
Where SAFAL Fits
SAFAL keeps supplier risk connected to the rest of the procurement lifecycle rather than isolated in a standalone assessment. Risk screening happens during supplier onboarding, financial health, sanctions exposure, and compliance documentation are assessed before activation, and that same supplier record carries forward into ongoing supplier performance management, where delivery, quality, and compliance signals continue to update the supplier’s profile rather than resetting at the next scheduled review.
Compliance documents carry automated expiry tracking through the supplier portal, so certification lapses surface as they happen rather than at the next audit. Because this all runs inside SAFAL’s Source-to-Pay platform, a supplier risk signal is visible to the same teams making the next sourcing and purchasing decision, not siloed in a separate risk system.
Conclusion
Supplier risk management has not changed in purpose. It still exists to keep a business from being blindsided by a relationship it depends on. What has changed is the pace suppliers actually operate at, and a once-a-year snapshot cannot keep up with risk that moves continuously.
The practical shift is not choosing monitoring over assessment. It is layering continuous signal tracking on top of the due diligence and periodic review an organization already runs, starting with the suppliers that would hurt most if something changed between reviews.
Frequently Asked Questions
Nikunj Soni
Nikunj Soni is Product Operations & Delivery Head at SAFAL, with 9 years of professional experience and a strong focus on product operations and enterprise solution delivery.